Bake Consent Into Your Design System With Cookie Banner Design
Bake Consent Into Your Design System With Cookie Banner Design
The right cookie banner gives every visitor a clear, equally weighted choice between “Accept,” “Reject,” and “Manage” without hiding the exit door, loads fast, and stays keyboard accessible. Placement matters less than parity: a footer bar or a modal both work if neither path to “no” costs more clicks than the path to “yes.” Design choices measurably move consent rates, which is exactly why testing (not guessing) belongs in your workflow, alongside proof points like WCAG focus rules and Coumba Win Design’s own build practice.
TL;DR:
- Equal visual weight for “Accept,” “Reject,” and “Manage” buttons is crucial, with avoidances of unequal path to decline that can be flagged as a dark pattern.
- Placement options such as footer, header, or modal depend on site type, but mobile layouts require testing to prevent experience degradation.
- Testing should measure how copy, button contrast, and placement influence consent, with layout tweaks having significant effects on refusal rates.
- For GDPR compliance, explicit opt-in is mandatory for EU/EEA visitors, whereas US laws like CCPA primarily use notice-and-out options; legal advice is recommended for complex situations.
- Accessibility requires visible focus control, correct ARIA roles, and early DOM placement; manual screen reader testing is essential before launch.
Table of Contents
- What Makes an Effective Cookie Banner Design
- Where Should a Cookie Banner Live on the Page?
- Design Elements That Actually Move Consent Rates
- GDPR vs. CCPA: What’s Actually Different?
- How Do You Make a Cookie Banner Accessible?
- Six Cookie Banner Patterns Worth Copying
- Best Practices for Multi-Language Cookie Banners
- Technical Implementation: Common Challenges and Fixes
- How to Test Cookie Consent UX Properly
- Updating Your Banner After a Policy Change
- Privacy-First Design Beyond the Legal Minimum
- Coumba Evelyn’s Perspective: Bake Consent Into the Design System, Not the Launch Checklist
- Get Your Cookie Banner Built Right the First Time
- Sources
- FAQ
What Makes an Effective Cookie Banner Design
Most cookie banners fail for one of two reasons: they’re either legally sloppy or they’re a UX disaster that tanks engagement before a visitor even sees your homepage. Good cookie banner design solves both problems at once, and the fix is less complicated than most teams assume.
Start with the copy. Visitors should understand in one glance what’s being tracked and why, without clicking through to a policy page just to figure out what “manage preferences” even means.
Here’s the checklist that separates a functional banner from a liability:
- Write plain-language copy (skip the legal jargon) with a visible link to your full privacy policy.
- Give “Accept,” “Reject,” and “Manage” equal visual weight, not a giant green button next to a gray text link.
- Keep toggles off by default in the preference panel, never pre-checked.
- Decide when consent gets recorded, how long it’s stored, and where a visitor can reopen settings later.
- Test the banner on a slow connection before shipping. If it delays your interactive page elements, that’s a UX cost hiding as a compliance win.
Unequal weighting between “accept” and “decline” is the single most common mistake, and it’s the one regulators flag most often.
Pro Tip: Build your banner as a component with defined states (open, minimized, reopened) instead of a one-off script. It saves you from rebuilding the whole thing every time your legal team updates the policy.
Where Should a Cookie Banner Live on the Page?
Placement isn’t cosmetic. It signals how much friction you’re willing to add between a visitor and your content, and it changes how visitors perceive your brand’s respect for their time.
- Footer bar: Slim, low-friction, ideal for content-first sites like blogs or news outlets where blocking the page hurts engagement more than it helps compliance.
- Header bar: Similar footprint to a footer bar but grabs attention faster; works well when brand visibility matters as much as consent capture.
- Modal or overlay: Forces a decision before continuing, which fits when your policy requires explicit opt-in before any tracking script fires.
- Cookie wall: Blocks all content until a choice is made; only defensible when there’s a genuine legal basis, and it’s the pattern most likely to draw regulatory attention.
On mobile, real estate is tight. A modal that eats the whole viewport on a phone screen creates a worse experience than the same modal on desktop, so test your layout at 375px width before calling it done.
Design Elements That Actually Move Consent Rates
This is where most teams guess instead of measure, and the guessing gets expensive. Copy, button emphasis, and framing aren’t just aesthetic decisions. They change outcomes at a scale that should make every product team pay attention.
The numbers: A large-scale experiment with 3,947 participants found that switching from neutral banner copy to consequence-based language (spelling out what accepting tracking actually does) raised the refusal rate from 16% to about 46%, nearly three times higher.
That’s not a rounding error. It means the words on your buttons are doing as much work as your legal team’s policy language, maybe more.
The same research flagged “unequal path to decline” as a specific risk pattern: banners that make “reject” require extra clicks, extra scrolling, or a buried menu. That’s a dark pattern, not a design choice, and it’s increasingly a compliance red flag on top of a trust problem.
What to test instead:
- Neutral versus consequence-based copy on the primary CTA.
- Button color and contrast between “accept” and “reject.”
- Placement of the “manage” link (inline text versus its own button).
Small layout tweaks alone can shift consent rates, so treat your banner like any other conversion surface: measure it, don’t just ship it once and forget it.
GDPR vs. CCPA: What’s Actually Different?
You don’t need a law degree to get the basics right, but you do need to know which model applies to your audience. The core difference is opt-in versus opt-out.
- GDPR and ePrivacy (EU/EEA visitors) require affirmative, granular opt-in before non-essential cookies fire. No pre-checked boxes, no implied consent from continued browsing.
- Typical US state laws like CCPA/CPRA lean on a notice-and-opt-out model: visitors get a “Do Not Sell or Share My Personal Information” link rather than a blocking banner.
- Build your checklist either way: visible policy link, stated purposes for each cookie category, storage duration, a clear way to withdraw consent, and vendor transparency for any third-party trackers.
- Loop in legal counsel when you’re sharing data with third parties, transferring data across borders, or touching special categories like health or biometric data.
Region-specific requirements shift often enough that a detailed compliance checklist is worth bookmarking rather than memorizing.
How Do You Make a Cookie Banner Accessible?
A banner that traps a keyboard user or gets skipped by a screen reader isn’t just an accessibility gap, it’s a legal exposure and a broken experience for a meaningful slice of your visitors.
- Keep focusable controls visible on screen; WCAG 2.2 explicitly requires that keyboard focus never gets hidden behind other content.
- Place the banner early in the DOM so tab order lands on it predictably, right after page load, not buried behind twenty other elements.
- Use ARIA roles correctly (
role="dialog"for a modal) and give screen readers a clear label for what the banner is asking. - Make the preference panel reopenable from a persistent, findable control, like a small footer icon, not a one-time popup that vanishes forever.
On performance, lazy-load anything non-essential and avoid triggering layout shifts when the banner appears or disappears.
Pro Tip: Run your banner through a screen reader once, manually, before launch. Automated accessibility scanners catch missing labels; they rarely catch a confusing focus order.
Six Cookie Banner Patterns Worth Copying
Every pattern below works for a specific site type. Pick based on your audience’s intent, not on what looks trendiest in a design gallery.
- Minimal footer with “Manage” link: fits content-heavy sites; low friction; test load-time impact on mobile.
- Branded modal with granular toggles: fits SaaS products needing explicit opt-in; builds trust through transparency; test toggle default states.
- Highlighted-decline for privacy-first audiences: fits niche or advocacy sites; signals respect for user choice; test whether it changes bounce rate.
- Consequence-language banner: fits transparency-focused brands; spells out what tracking does; test refusal rate against a neutral-copy version.
- Compact header bar for news sites: fits fast-scroll content; stays out of the reading flow; test scroll-depth impact.
- Quick “essential-only” modal: fits e-commerce checkout flows; speeds up the decision; test conversion impact on the buy path.
Vendor galleries like OneTrust’s example collection are useful for visual inspiration, though copying a competitor’s UI verbatim won’t guarantee compliance for your specific data flows.
Best Practices for Multi-Language Cookie Banners
If your site serves visitors across regions, your banner needs to speak their language, literally, not just legally. A banner that auto-detects browser or IP-based locale and swaps copy accordingly avoids the awkward scenario of a French visitor reading English legal text they can’t parse.
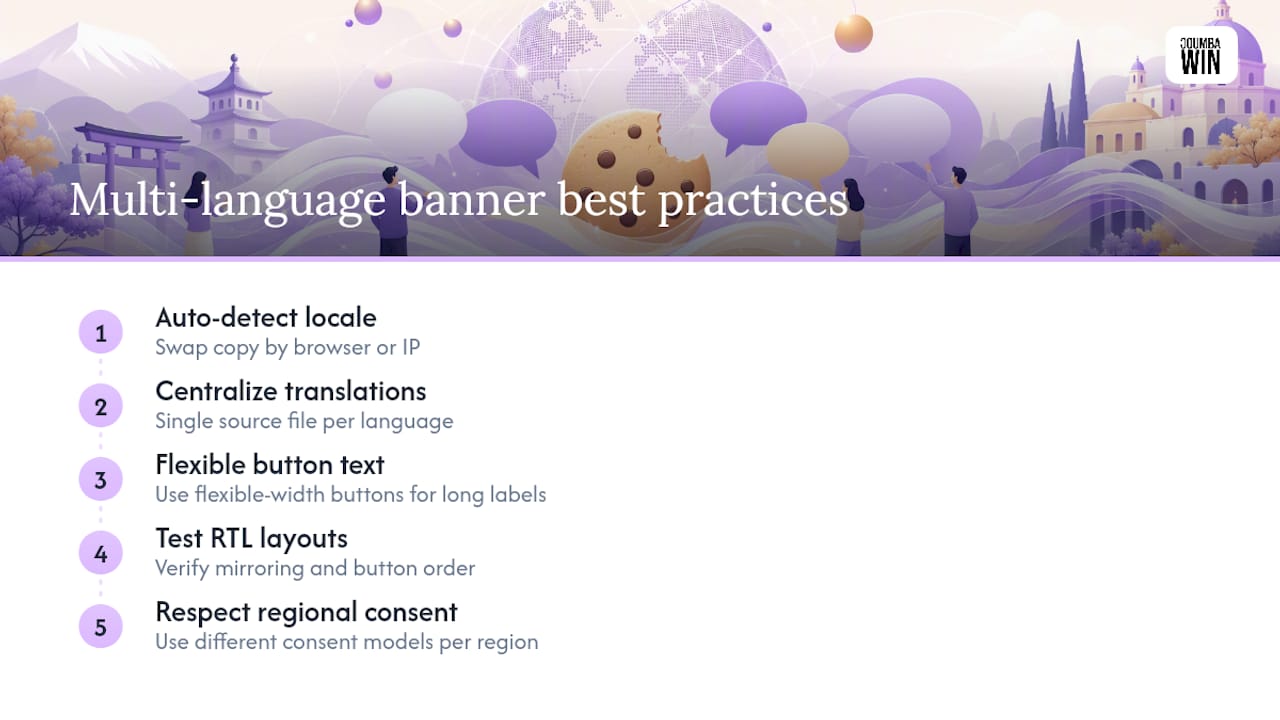
Keep translated strings in a centralized file rather than hardcoded per page. This matters more than it sounds: when your privacy policy updates, you want one source of truth for every language variant, not five different translators working from five different drafts.
Button labels need the same care as body copy. “Accept” and “Reject” translate differently across languages in terms of formality and length, and a translated button that overflows its container looks broken even when the underlying logic is sound. German and Finnish, for example, tend to produce noticeably longer button text than English, so build flexible-width buttons rather than fixed-pixel ones.
Test right-to-left languages separately if your audience includes Arabic or Hebrew readers. A banner that mirrors correctly for Latin scripts often breaks silently for RTL layouts, with buttons landing in the wrong visual order relative to reading direction.
Finally, don’t assume one legal framework covers every language variant. A banner serving both EU and US visitors in French and English respectively may need two different consent models entirely, not just two translations of the same logic.
Technical Implementation: Common Challenges and Fixes
The gap between “designed a good banner” and “shipped a working banner” is where most teams lose weeks. A handful of recurring problems account for most of the pain.
Consent management platform integration is the first hurdle. Tag managers need to hold third-party scripts until consent is granted, which means your analytics, ad pixels, and chat widgets all need conditional loading logic, not a fire-and-forget script tag dropped in the header.
Consent persistence across sessions and subdomains trips up more teams than it should. If your marketing site lives on one subdomain and your app on another, a visitor who consents on one shouldn’t have to repeat the process on the other, but syncing that state correctly takes deliberate architecture, not an afterthought.
Layout shift is the quiet performance killer. A banner that injects itself into the DOM after the page has already rendered pushes content around, which hurts your Core Web Vitals score and irritates anyone mid-scroll when it appears.
Third-party script timing matters too. Some vendor scripts fire before your consent logic even initializes, which defeats the entire purpose of the banner. Test this specifically. It’s the failure mode audits catch most often, and it’s invisible from the front end unless you’re inspecting network requests.
Building the consent logic as a reusable component, the same way you’d build any other interactive front-end module, solves most of these problems once instead of repeatedly.
How to Test Cookie Consent UX Properly
Testing a cookie banner isn’t the same as testing a checkout flow, mostly because the metric you care about (consent rate) is adversarial by nature: you’re measuring how often people say no to something, not yes.
Start with A/B testing on copy and button emphasis, holding everything else constant. Change one variable at a time, whether that’s neutral versus consequence-based language or button color contrast, so you know exactly what moved the number.
Session recordings reveal friction that surveys never will. Watching where visitors hover, hesitate, or abandon the page entirely after the banner appears tells you more than a satisfaction score.
Run moderated usability tests with a handful of real users if you can. Ask them to find the “manage preferences” option without prompting; if they can’t locate it in under ten seconds, your hierarchy needs work.
Track downstream metrics too, not just the click on the banner itself. Bounce rate immediately after banner display, time-to-first-interaction, and scroll depth all signal whether your banner is a minor speed bump or a genuine barrier.
Finally, test across devices and connection speeds. A banner that performs fine on a fast desktop connection can feel sluggish and janky on a throttled mobile connection, exactly the environment where consent rate matters most because that’s where most traffic lives.
Updating Your Banner After a Policy Change
Privacy policies change more often than most teams plan for, whether it’s a new vendor integration, an updated data-sharing agreement, or a regulatory shift in a market you serve. Your banner needs a process for that, not a scramble.
Version your consent records. When you update what a “yes” actually means (say, adding a new third-party tracker), old consent shouldn’t silently apply to new data uses. Re-prompt visitors whose consent predates the change.
Set a re-consent trigger tied to policy version number, not a calendar date. A visitor who consented under policy version 3 should see a fresh prompt when version 4 introduces a materially different data practice, regardless of how much time has passed.
Keep a changelog, even an internal one, mapping banner copy changes to policy changes. When someone asks “why did refusal rates jump last quarter,” you want an answer faster than a code archaeology dig through six months of commits.
Communicate substantive changes clearly in the re-prompt itself. A banner that says “we’ve updated our practices” without saying what changed forces visitors to either blindly accept or dig through a policy page, and most will just click whatever’s easiest, which defeats the point of asking again.
Privacy-First Design Beyond the Legal Minimum
Compliance sets the floor, not the ceiling. The sites that earn genuine trust treat consent as a relationship, not a checkbox exercise.
Default to collecting less. Every cookie category you don’t need is one less thing to justify, one less line in your policy, and one less reason a visitor hesitates before clicking “accept.” Audit your tracking stack annually and cut anything that isn’t earning its place.
Make your data practices legible without requiring a law degree to parse them. A privacy policy written in plain English isn’t just good UX, it’s a competitive signal in a market where visitors increasingly notice which brands respect their attention and which ones bury the fine print.
Give visitors real control after the initial decision, not just at the moment of first visit. A settings page that’s easy to find and quick to update signals that you view consent as ongoing, not a one-time hurdle to clear before the “real” experience begins.
Coumba Evelyn’s Perspective: Bake Consent Into the Design System, Not the Launch Checklist
Most teams treat the cookie banner as a launch-week fire drill, then forget it exists until legal flags a problem. That’s backward. Treating consent UI as a permanent component, with defined tokens, focus states, and a reopenable settings hook, means it survives redesigns instead of breaking every time your homepage changes. Build it once, test it like any other interactive design system component, and it stops being a recurring fire drill.
— Coumba Evelyn
Get Your Cookie Banner Built Right the First Time
Coumba Win Design treats your consent banner as a real design problem, not a compliance afterthought bolted on after launch. That means it gets the same strategic attention as your homepage hero or your pitch deck, built to match your brand’s actual visual system instead of a generic plugin default.
Startups working with Coumba Win Design get banner copy, button hierarchy, and accessibility checks handled as part of the same engagement that builds your site or product UI, so nothing ships looking like an afterthought stapled onto a polished brand. The team’s component-based development approach means your consent controls get built once, correctly, and reused across every page without drifting out of sync with your design system. Curious what that looks like for your product? Visit Coumba Win Design and get a project scoped out.
Sources
- Design parameters and large-sample experiment on consent banner design (Bielova et al., USENIX Security 2024)
- Cookie UX: How to ask users for their cookies (LogRocket Blog)
- Cookie Banner UI & UX Checklist (CookieChimp)
FAQ
How Do You Create a Cookie Banner?
Start with plain-language copy, equal-weight “Accept,” “Reject,” and “Manage” buttons, and a visible policy link, then implement it as a lightweight, accessible component that loads early in the page and integrates with your tag manager to hold third-party scripts until consent is granted.
Is It Illegal Not to Have a Cookie Banner?
It depends on your audience and data practices: EU/EEA visitors generally require a consent mechanism under GDPR and ePrivacy rules, while US requirements vary by state and often focus on opt-out notices rather than a mandatory banner for every site.
What Should a Cookie Banner Say?
It should state plainly what data gets collected, why, and for how long, with clear, equal options to accept, reject, or manage preferences, plus a working link to the full privacy policy.
What Is the Purpose of a Cookie Banner?
It gives visitors informed, actionable control over tracking before it happens, satisfying legal consent requirements while signaling that a site respects visitor choice rather than burying it.